


TOKYO –
The Japanese authorities is getting ready to ascertain a brand new cybersecurity response crew comprising specialists from the private and non-private sectors, with plans to dispatch specialists to firms and organizations going through critical cyberattacks following a collection of unauthorized intrusions and data leaks.
The authorities is predicted to convene a gathering of related Cabinet ministers as early as November 6 to announce a package deal of emergency measures aimed toward combating unauthorized entry to laptop methods.
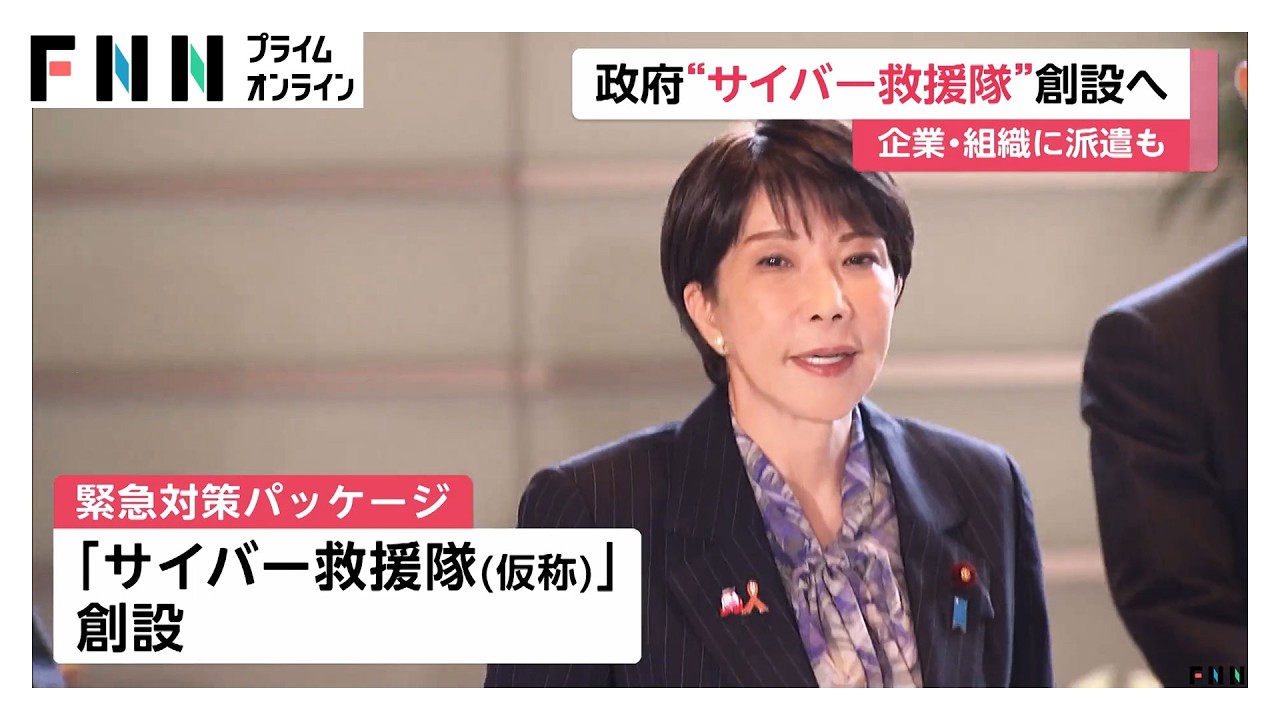
According to authorities officers, the package deal will embody the creation of a provisional “Cyber Rescue Team,” bringing collectively cybersecurity specialists from authorities companies and personal firms. The crew could be dispatched to companies and different organizations when pressing help is deemed mandatory.
The initiative comes as repeated cyberattacks and information breaches have raised considerations over the power of firms and establishments to guard delicate info and reply successfully to safety incidents.
The authorities additionally plans to advertise wider use of safe identification verification by means of the My Number Card system, Japan’s nationwide identification program, as a part of efforts to strengthen safety in opposition to unauthorized entry.
Another proposed measure entails cooperation with abroad synthetic intelligence firms to make use of superior AI know-how to gather and consolidate info on vulnerabilities in laptop methods.
By combining specialist response groups, stronger identification verification and AI-powered vulnerability evaluation, the federal government goals to enhance Japan’s skill to forestall cyberattacks and reply rapidly when safety breaches happen.
The authorities’s transfer follows a wave of main cyberattacks affecting a few of Japan’s largest firms, with breaches more and more spreading by means of exterior know-how suppliers. In October, East Japan Railway reported that roughly 6.09 million buyer accounts might have been compromised, whereas Kyushu Railway disclosed a possible breach involving one other 1.3 million accounts. Both incidents have been linked to a ransomware assault concentrating on IDC Frontier, a cloud providers subsidiary of SoftBank, highlighting the dangers posed when firms depend on shared know-how infrastructure.
Other main incidents disclosed in October included a attainable leak of private info belonging to as many as 6.43 million clients of secondhand retailer Bookoff and roughly 8.72 million clients of Daiichikosho, which operates the Big Echo karaoke chain. Travel reserving operator Adventure, which runs the Skyticket platform, additionally reported that roughly 14.64 million units of private info might have been uncovered following unauthorized entry to its methods. The affected firms stated that they had discovered no proof of misuse of the knowledge on the time of their bulletins.
The assaults continued into November, with electronics retailer Nojima reporting a breach probably involving roughly 7 million buyer information, whereas cosmetics platform @cosme disclosed unauthorized entry affecting about 3 million customers. Suntory Holdings additionally reported that an exterior cloud service breach had uncovered names, electronic mail addresses and different info regarding roughly 90,000 individuals, together with workers. The incidents have raised considerations over the safety of buyer databases and the rising dependence of main firms on third-party cloud providers.
Another vital incident concerned electronic mail distribution supplier Arara, which disclosed a breach affecting roughly 77 million electronic mail tackle information. The assault had repercussions for quite a few firms utilizing its providers, together with retailers, meals firms and different companies that relied on exterior suppliers to speak with clients. The incident illustrates how an assault on a single know-how provider can expose info held on behalf of lots of of organizations, creating dangers far past the unique goal.
The rising scale and frequency of those incidents have intensified strain on the federal government to strengthen Japan’s cybersecurity defenses. Many firms, notably smaller companies, lack the specialist personnel wanted to research subtle intrusions, comprise harm and restore compromised methods. The proposed Cyber Rescue Team is meant to assist tackle that scarcity by making public- and private-sector experience obtainable when organizations face critical safety emergencies.
Source: FNN