


TOKYO –
Japan is dealing with a pointy enhance in cyberattacks, with specialists warning that synthetic intelligence is making it simpler for criminals to steal and exploit private data, whereas the rising sophistication of on-line fraud is exposing weaknesses within the nation’s cybersecurity defenses.
An worldwide hacking group generally known as Qilin has described Japan as “one of the countries with the weakest computer security in the world,” a declare that displays rising issues over the frequency of assaults concentrating on Japanese companies and organizations.
Research by Yutaka Sejiyama, assistant director of the Macnica Security Research Center, exhibits that the variety of publicly disclosed incidents involving data leaks brought on by cyberattacks in Japan has been growing since July.
By October 9, the nation had already recorded 25 such incidents through the month. If the present tempo continues, the month-to-month whole might exceed 70, highlighting the accelerating risk to company networks and private knowledge.
Sejiyama believes AI is enjoying a major position within the enhance. “Judging from the circumstances, there is no doubt that AI is being extensively used,” he mentioned.
However, the expertise being exploited by cybercriminals could differ from acquainted client AI providers reminiscent of ChatGPT and Gemini.
According to Sejiyama, attackers are seemingly utilizing AI fashions described as “open-weight,” which permit customers appreciable freedom to customise their operation.
Open-weight fashions present entry to the underlying parameters that decide how an AI system features, making it attainable to switch or adapt the expertise for a variety of functions. Although this flexibility helps reliable analysis and business purposes, it will also be exploited to develop instruments for cyberattacks.
By distinction, business AI providers reminiscent of ChatGPT usually place better restrictions on how their programs may be personalized and used, offering safeguards supposed to restrict malicious purposes.
The increasing risk isn’t restricted to the preliminary theft of knowledge. Experts warn that AI can also be growing the worth of stolen private knowledge by making it simpler for criminals to mix separate items of knowledge and establish alternatives for fraud.
Recently disclosed leaks involving photos of driver’s licenses illustrate the dangers. Criminals who acquire such data could possibly impersonate victims, apply for loans from client finance corporations with out their information, or make costly purchases utilizing their identities.
Stolen private data can also be purchased and bought on the darkish net, part of the web accessible via specialised software program and regularly related to illicit marketplaces.
Even data that seems comparatively innocent when thought of by itself can develop into beneficial when mixed with different leaked data.
For instance, a prison who obtains an individual’s title and e-mail deal with could initially have restricted alternatives to take advantage of the knowledge. However, if these particulars may be linked to a different database containing the identical individual’s title and bank card quantity, the potential for fraud will increase significantly.
Additional data exhibiting journey reservations, reserving dates, and passwords for reservation web sites can present criminals with an much more detailed image of a sufferer’s actions.
AI is especially efficient at figuring out connections amongst massive volumes of fragmented knowledge, permitting attackers to assemble particular person data into extra complete private profiles.
This functionality additionally makes it attainable to investigate victims’ habits and decide when fraudulent communications are most probably to seem reliable.
Rather than sending indiscriminate phishing emails, criminals can tailor messages to match an individual’s precise actions and circumstances, growing the probability that the recipient will reply with out suspicion.
In September, for instance, individuals who had made real lodging reservations acquired fraudulent emails containing their precise reserving data. The messages instructed recipients to reenter their bank card particulars or make pressing funds.
Because the emails included reliable reservation particulars, recipients might have mistaken them for genuine communications from lodging suppliers or reserving platforms.
Such incidents exhibit how stolen data can be utilized not just for direct id theft but in addition to create extremely convincing scams that exploit the belief folks place in acquainted business transactions.
With cyberattacks turning into extra frequent and private data leaks more and more troublesome to stop, specialists say people must strengthen the safety of their on-line accounts.
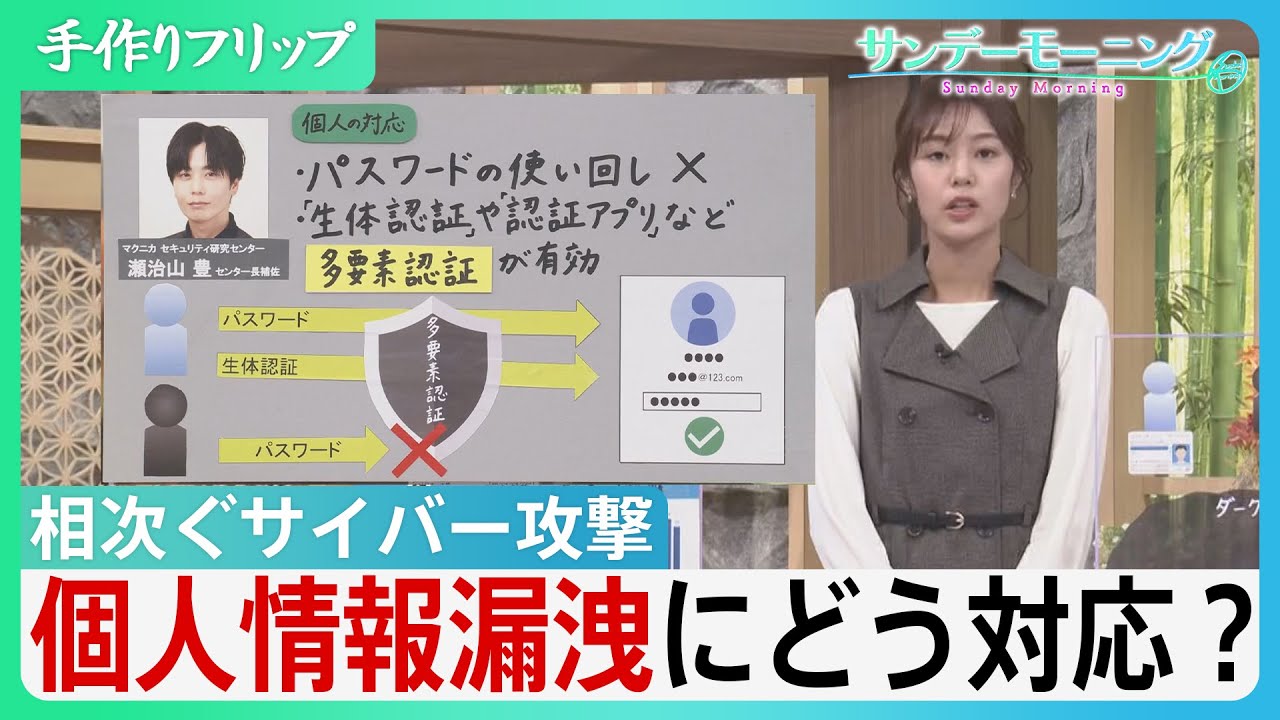
Sejiyama recommends avoiding the reuse of passwords throughout completely different providers and actively enabling multifactor authentication wherever it’s out there.
“Naturally, people should not reuse passwords, but it is also effective to actively use multifactor authentication, such as biometric verification or authentication apps, on websites that support it,” he mentioned.
Multifactor authentication requires customers to offer an extra type of verification past a password, reminiscent of biometric identification or affirmation via a devoted authentication utility.
Once enabled, a password alone is now not adequate to entry an account. Even if login credentials are uncovered in a knowledge breach, the extra safety requirement can considerably cut back the danger of unauthorized entry.
The measure is especially vital as criminals develop into more and more able to linking data obtained from a number of breaches and utilizing it to focus on people via customized assaults.
The fast progress of AI-assisted cybercrime is creating a brand new problem for Japan’s digital economic system, the place the safety of private data relies upon not solely on the defenses maintained by corporations but in addition on the precautions taken by particular person customers.
As attackers undertake more and more subtle expertise, specialists emphasize that conventional password safety alone is now not sufficient, making stronger authentication and better consciousness of knowledge safety important defenses towards on-line fraud.
Source: TBS