


TOKYO –
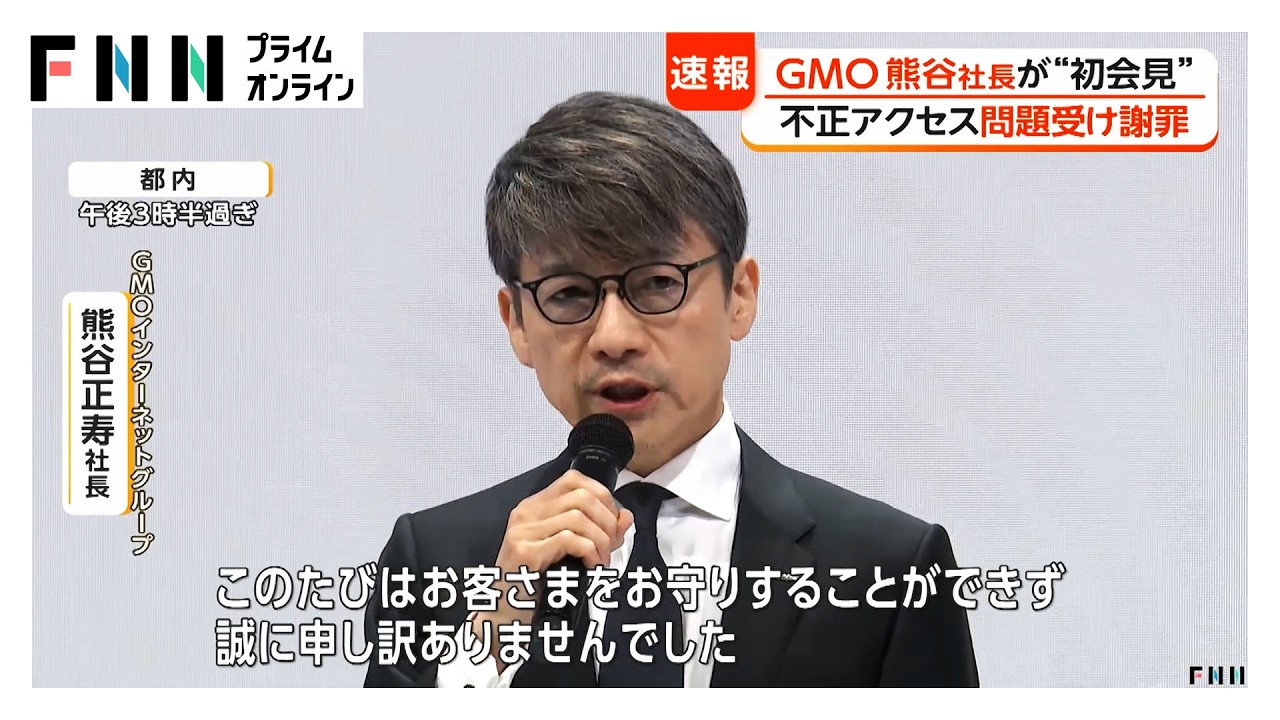
GMO Internet Group President Masatoshi Kumagai apologized at his first press convention following a cyberattack on the corporate’s investor-oriented cloud service, acknowledging that safety vulnerabilities had been recognized by specialists throughout the group two years earlier however that the warnings had not been adequately addressed.
“We sincerely apologize to all customers and related parties who have suffered damage,” Kumagai mentioned. “Our group’s Onamae.com Desktop Cloud service was subjected to unauthorized access, resulting in the leakage of customer information and, ultimately, the loss of customer assets through malicious activity.”
The firm confirmed the cyberattack on October 20, when unauthorized entry was found involving a service utilized by traders. The incident escalated final week when hackers publicly launched private info believed to belong to one of many service’s customers, elevating issues in regards to the extent of the breach and the potential for additional injury.
During the press convention, Kumagai acknowledged that the affected system had safety weaknesses and revealed that specialists at GMO Cybersecurity by Ierae, a cybersecurity firm throughout the identical company group, had recognized issues roughly two years earlier.
“It is true that there were security problems with this service’s system,” Kumagai mentioned. “It is also true, as has been reported, that experts at our group’s GMO Cybersecurity by Ierae had pointed out issues with the system.”
Kumagai admitted that the corporate had failed to include these warnings into the administration and operation of the service.
“We were unable to make use of the issues identified within our own group in operating the service,” he mentioned, apologizing for the corporate’s failure to take applicable preventive motion.
The admission raises questions on GMO’s inside danger administration and the effectiveness of communication between its cybersecurity specialists and the enterprise divisions chargeable for working buyer providers.
GMO Internet Group operates a variety of web infrastructure, area registration, monetary know-how and cybersecurity companies. The affected Onamae.com Desktop Cloud service supplies cloud-based desktop computing environments, together with methods utilized by traders for monetary buying and selling.
The assault has attracted specific consideration as a result of the compromise of an investor-oriented service can expose clients not solely to the theft of private info but in addition to potential monetary losses if attackers receive entry to buying and selling environments or different delicate account info.
Meanwhile, a senior GMO government instructed JNN on the morning of November 2 that investigators had uncovered numerous leads regarding the unauthorized entry.
“Various clues are emerging,” the manager mentioned.
Investigators are inspecting a number of prospects, together with the potential involvement of a North Korean-linked hacking group. However, no definitive attribution has been introduced, and the id of these accountable stays beneath investigation.
The risk of North Korean involvement has added a world safety dimension to the incident, significantly given the historical past of cyberattacks attributed to North Korean teams focusing on monetary establishments, cryptocurrency companies and different organizations dealing with helpful monetary property.
The disclosure that safety issues had been raised internally two years earlier than the assault can also be prone to intensify scrutiny of GMO’s company governance and the steps taken to guard buyer info and monetary property.
The press convention was persevering with on the time of the report, with consideration centered on how a lot the corporate would disclose in regards to the proof collected throughout its investigation, the circumstances that allowed the safety weaknesses to stay unresolved, and the measures being taken to stop additional injury.
Source: TBS